الحوسبة السحابية
3 min readBack to blog
In many IT projects, organizations reach a stage where expanding their server and network infrastructure becomes essential, only to hit the roadblock of building an on-premises data center. The operational overhead of backup generators, precision cooling, clean-agent fire suppression, and industrial power permits often creates a massive financial burden—frequently exceeding the cost of the hardware itself.
This is where colocation (Co-Location) services emerge as a balanced engineering approach: the organization retains full ownership and control of its physical equipment, while the provider delivers a secure, highly reliable operating environment within an enterprise-grade data center facility.
Colocation goes far beyond renting rack space; it provides an integrated facilities ecosystem engineered to sustain uninterrupted operations according to global standards:
Power Redundancy: Independent dual power feeds (Feed A / Feed B) backed by uninterruptible power supplies (UPS) and standby diesel generators. This ensures that servers equipped with dual power supplies remain fully operational even during a complete outage on one utility line.
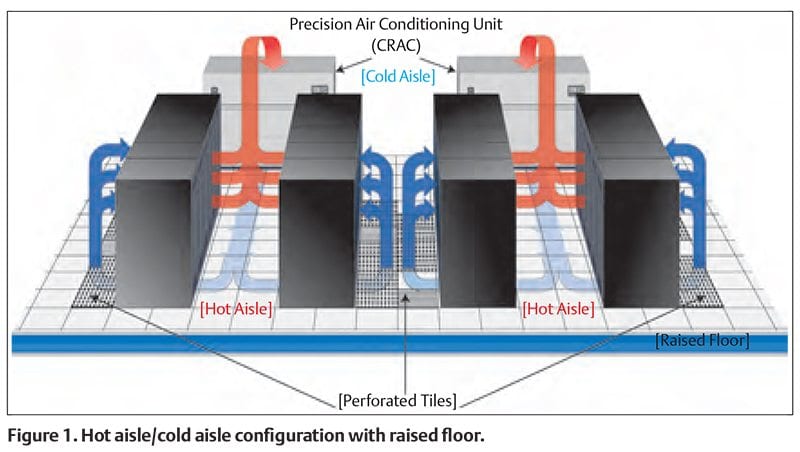
Precision Cooling: Precise climate and humidity regulation adhering to hot/cold aisle containment standards, protecting processors and sensitive components from thermal stress.
Physical Security: Multi-layered access controls, including 24/7 CCTV surveillance, biometric entry points, individually locked cabinets, and comprehensive audit logs.
Fire Detection and Suppression: Very Early Smoke Detection Apparatus (VESDA) combined with clean-agent suppression systems (such as FM-200 or Novec 1230) to eliminate fire hazards without damaging electronic circuitry.
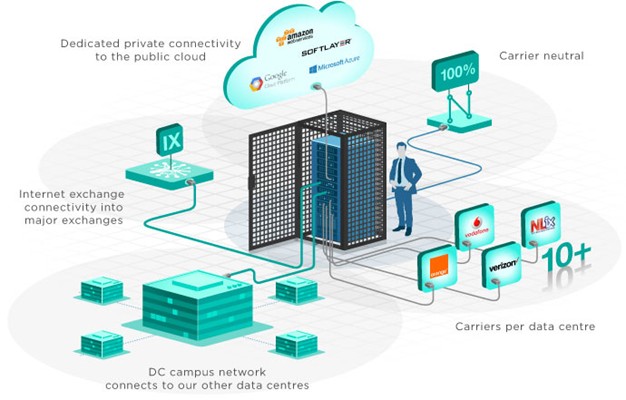
A decisive differentiator among colocation facilities is carrier neutrality. A carrier-neutral data center allows you to connect your rack to multiple Internet Service Providers (ISPs) via cross-connects, whether over fiber or copper cabling.
This capability empowers network engineers to configure multi-homed BGP routing and deploy redundant internet uplinks or MPLS circuits from diverse providers, ensuring end-to-end network resiliency without vendor lock-in.
Rack Layout and Power Planning:
Before dispatching servers and storage arrays, calculate the aggregate power consumption in kilowatts (kW) and ensure compatibility with the rack's power distribution unit (PDU) ratings. Always place heavier equipment—such as SAN arrays and blade chassis—at the bottom of the cabinet, reserving the top rack units (RU) for switches and patch panels.
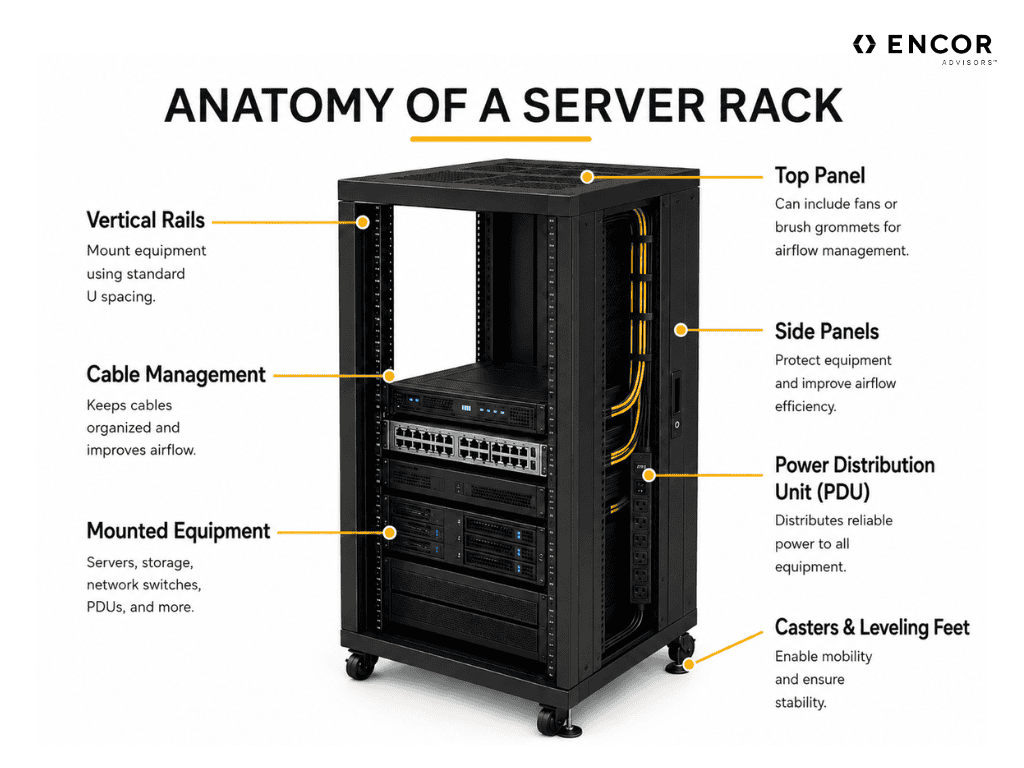
Cable Management and Port Labeling:
Cable organization inside the rack is critical to performance, not just aesthetics. Poor routing disrupts cold airflow and drives up internal temperatures, while complicating physical troubleshooting. Every cable must be neatly dressed and clearly labeled at both termination points prior to racking.
Out-of-Band Management and Remote Hands:
Because the hardware is not within walking distance, configuring dedicated out-of-band management interfaces (such as Dell iDRAC or HPE iLO for servers, and serial console ports for switches and firewalls) over a secure VPN is vital. For hardware incidents requiring physical intervention—such as hard power cycles or hot-swapping a failed drive—data center Remote Hands technicians can execute tasks on your behalf.
Ultimately, colocation remains the optimal architecture for organizations mandated to maintain direct physical custody of their data assets, while eliminating the operational risk and complexity of building and maintaining an internal data center facility.
Be the first to rate this article
Learn about Containers as a Service (CaaS) and how it helps organizations easily deploy, run, manage, and scale applications within cloud computing environments.
A practical engineering perspective illustrating the core difference between traditional firewalls and WAFs, explaining why Layer 4 protection and NGFWs fall short in securing web applications and APIs, alongside a practical review of deployment models and false positive challenges.
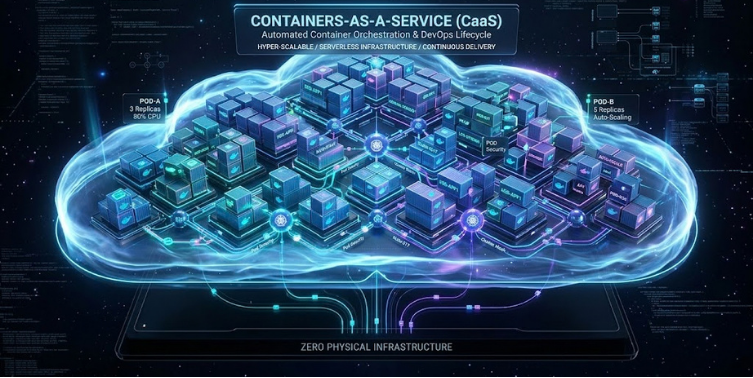
Containers as a Service (CaaS) is an advanced cloud computing model. This technology enables developers and operations teams to deploy and manage containerized applications using popular build tools such as Docker. It also relies on advanced orchestration and automation engines such as Kubernetes to manage these containers and their clusters, and to scale them automatically as needed. Thus, the platform relieves organizations of the complexities of managing physical infrastructure, enabling them to focus entirely on software development efficiently and securely.